Sales Inquiries: (855) 634-5557
Helpdesk: (818) 249-1963
CMMC Compliance Services in Los Angeles
CMMC compliance is essential for DoD contractors to win and retain federal contracts. GenCare implements and manages CMMC Level 2 technical controls, keeps your evidence audit-ready, and provides the hands-on CMMC consulting your team needs to meet its compliance requirements, all backed by a trusted Southern California team serving LA businesses since 1986.
471
projects completed

100%
employee-owned

180
years combined tenure

278
active clients

What is CMMC compliance, and why does it matter for your contracts?
CMMC stands for Cybersecurity Maturity Model Certification. It is the Department of Defense framework that verifies a contractor protects sensitive federal data before a contract is awarded. If your company handles Federal Contract Information or Controlled Unclassified Information anywhere in the Defense Industrial Base (DIB), a CMMC requirement will appear in your contracts, and your ability to bid depends on meeting it.
For most contractors and subcontractors, that means CMMC Level 2, which maps directly to the 110 security controls in NIST SP 800-171. Reaching Level 2 is not a one-time project. It is a set of technical safeguards, written policies, and ongoing evidence that together prove your systems meet the standard. That is the work GenCare takes off your plate.
Here is what our CMMC engagement covers:
Implementation and management of the technical controls that make up the majority of NIST SP 800-171.
A secured Microsoft 365 environment, with GCC High deployed when your contracts require it.
Endpoint and identity hardening, multi-factor authentication, logging, and continuous monitoring.
Backup, recovery, and vulnerability management built to the standard and documented.
Security awareness training and simulated phishing for your staff.
A living System Security Plan and Plan of Action and Milestones, kept current as your environment changes.
Support through your self-assessment or third-party assessment, with the evidence organized and ready.
The Three CMMC Levels, and Where Your LA Business Fits
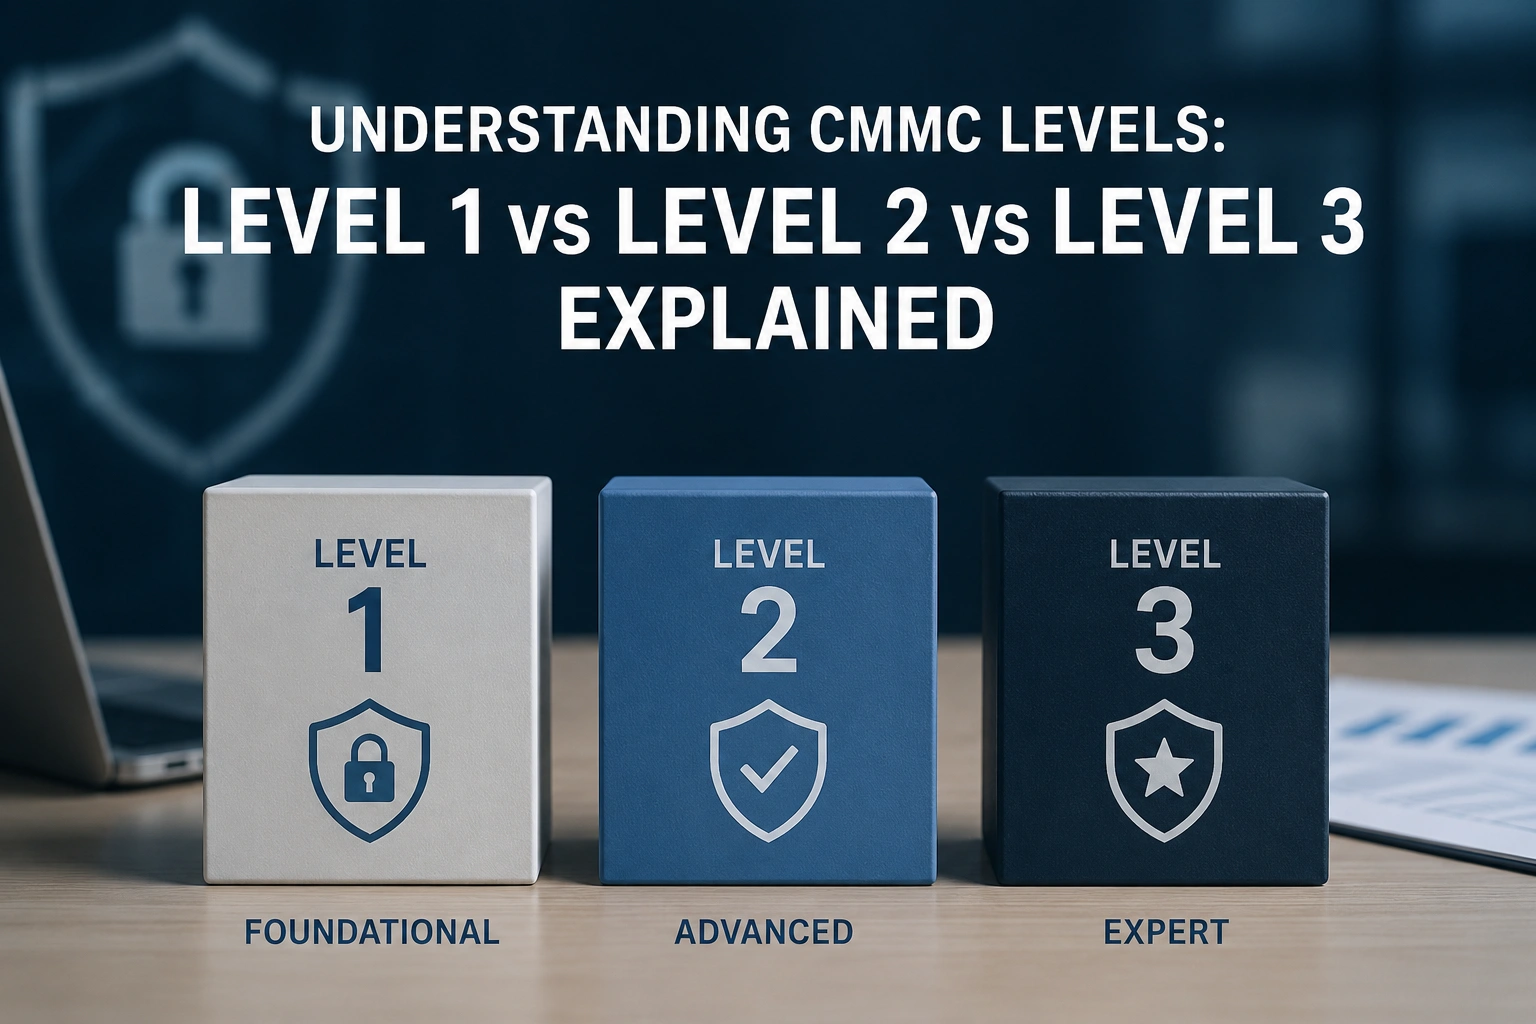
CMMC 2.0 sets three levels of maturity, and the level you need depends on the sensitivity of the data your contracts touch. Knowing your level early prevents over-building controls you do not need and under-preparing for the ones you do.
Level 1 (Foundational) applies to contractors that handle only Federal Contract Information. It covers 17 basic safeguards and is met through an annual self-assessment. Level 2 (Advanced) applies to the much larger group of contractors handling Controlled Unclassified Information, and it requires all 110 controls from NIST SP 800-171. Level 3 (Expert) is reserved for a small number of programs with the highest-priority information and adds controls from NIST SP 800-172.
Most Los Angeles defense contractors and subcontractors land at Level 2. That is GenCare's focus, and it is where the technical lift behind CMMC certification is heaviest.
Self-assessment or third-party certification: which path is yours?
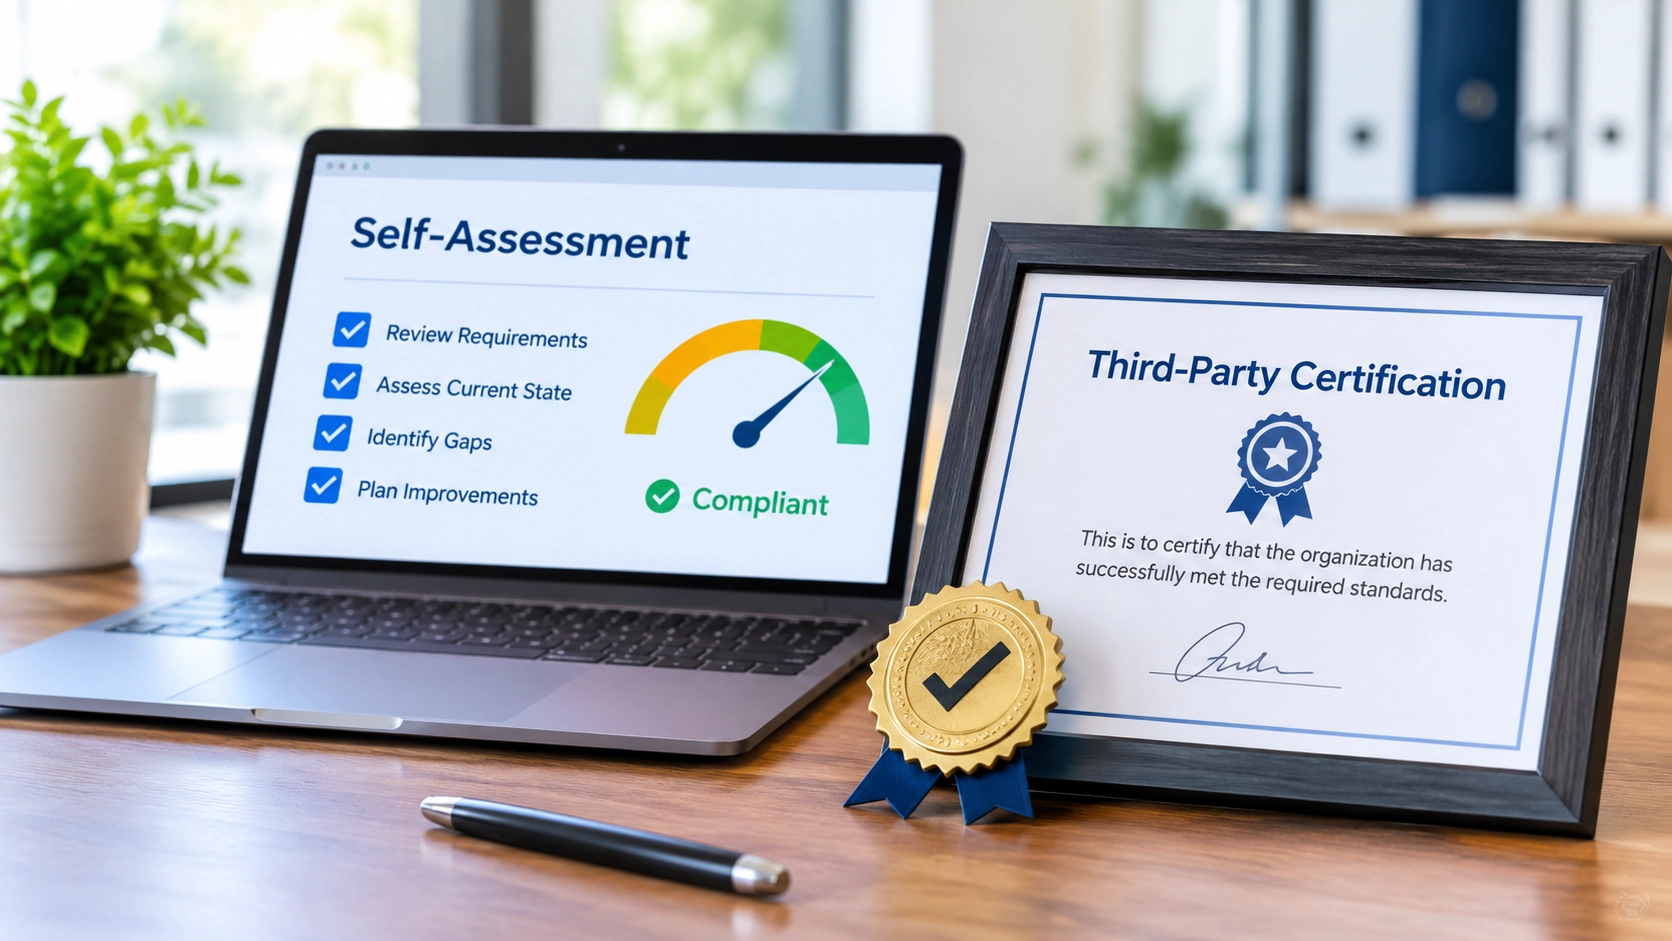
CMMC Level 2 has two paths, and the one that applies is written into your specific contract. Some Level 2 acquisitions allow an annual self-assessment, where your company attests to meeting all 110 controls and files the result. Others require CMMC Level 2 certification through an accredited third-party assessment organization, known as a C3PAO, on a three-year cycle.
Either way, the underlying work is the same: every control implemented, every policy written, and every piece of evidence in order. GenCare prepares you so the path your contract names is a formality rather than a scramble. When an assessor or C3PAO is involved, we sit in those conversations as your External Service Provider (ESP), show the technical evidence, and make adjustments to keep you on track.
Where GenCare Fits, and Where You Stay in Control
CMMC compliance involves both technical security measures and responsibilities that must remain with your internal team. As your CMMC MSP, GenCare makes these roles clear so nothing falls through the cracks.
What GenCare Handles
We take ownership of the technical controls required for CMMC Level 2, including:
Microsoft 365 and identity security
Device enrollment and management
Security logging and monitoring
Backup and disaster recovery
Vulnerability management
Security awareness training
We also manage regular meetings, assign tasks, document progress, and compile evidence for your System Security Plan (SSP) and Plan of Action and Milestones (POA&M).
What Your Team Handles
Certain responsibilities must remain with your organization, including:
Defining internal roles and responsibilities
Employee screening and training
Physical security of your facilities
We guide your team through each requirement during regular meetings, ensuring responsibilities are clearly defined and completed.
What to Expect
Most contractors should plan for approximately five hours per week during the implementation phase: one hour of direct collaboration with GenCare and the remaining time dedicated to assigned internal tasks.
Real results from Los Angeles organizations
Defense readiness is built on the same fundamentals that protect every client we serve: tight security, fast response, and a team that sweats the details. Here is what local organizations say about working with GenCare.
"Our systems are a lot more secure."
Libby, Library Foundation of Los Angeles, managed IT services client
"GenCare works with a sense of urgency but never loses sight of the details."
Alicia, J's Maintenance, post-breach recovery client
"Excellent response time and very helpful in addressing and fixing a login issue."
Michael H, GenCare client
Know Your CMMC Scope Before You Invest
Not every system, device, or employee needs to fall within your CMMC assessment boundary. GenCare starts with a CMMC gap assessment that measures your current controls against NIST SP 800-171, then helps you identify where Controlled Unclassified Information (CUI) lives, determine what needs protection, and define a clear path to CMMC Level 2 compliance.
Start with a no-cost, 30-minute readiness call and understand your scope before spending on controls you may not need.
The hidden risk: controls that drift out of compliance
Passing once is not the hard part. Staying compliant is. Contracts renew, staff changes, laptops get replaced, and a control that was in place in January can quietly fall out of alignment by summer. When your self-assessment or next audit comes due, that drift becomes a finding, and a finding can stall a contract.
GenCare delivers managed CMMC compliance as an ongoing service rather than a project with an end date. We continuously remediate vulnerabilities, re-test your people with simulated phishing, validate that each safeguard still holds, and keep your evidence current. Your cybersecurity services in Los Angeles and your compliance posture move together, not on separate tracks.
The scoping gap: not knowing what counts as in-scope
The fastest way to blow a CMMC budget is to secure your entire company when only part of it touches Controlled Unclassified Information. Contractors who skip scoping either overspend hardening systems that never see CUI, or under-prepare and fail on the systems that do.
We start every engagement by mapping where your CUI lives: where it originates, how it moves, and which users, devices, and applications handle it. That map sets your assessment boundary, keeps the project affordable, and makes your managed IT services across Greater Los Angeles work in step with your compliance plan instead of against it.
What GenCare handles for your CMMC Level 2

Microsoft 365 and GCC High security
We secure the environment where most of your Controlled Unclassified Information lives, and deploy the government cloud when your contracts call for it.
Configure Microsoft 365 to the NIST SP 800-171 baseline
Deploy and manage GCC High when a contract requires it
Lock down sharing, data loss prevention, and external access

Identity and access control
Access control is the heart of NIST SP 800-171, and it is where assessments most often fail. We make sure the right people reach the right data and no one else.
Enforce multi-factor authentication across all accounts
Apply least-privilege roles and conditional access
Review and document access on a set schedule

Endpoint enrollment and hardening
Every device that touches your data is a control point. We enroll and harden them, and block the ones that are not enrolled.
Enroll devices and apply security baselines with Intune
Stop un-enrolled devices from reaching your network
Encrypt drives and manage patching continuously

Logging, monitoring, and audit evidence
CMMC requires proof, not promises. We capture the logs and monitoring the standard demands and turn them into evidence.
Centralize security logs across systems and identities
Monitor for and respond to suspicious activity
Retain records that satisfy assessment requirements

Backup, recovery, and resilience
Recoverability is a graded control and a business necessity. We build backup and recovery to the standard and test it.
Configure backup and recovery controls to NIST SP 800-171
Test restores so recovery is proven, not assumed
Document the process for your System Security Plan

Vulnerability and risk management
Threats move; your defenses have to move with them. We find and fix weaknesses before an assessor or an attacker does.
Scan for and remediate vulnerabilities on a schedule
Prioritize fixes by real risk to your CUI
Track remediation in your Plan of Action and Milestones

Security awareness training
People remain the most tested control. We train your staff and keep testing them so the human layer holds.
Deliver role-based security awareness training
Send simulated phishing and coach from the results
Record completion as compliance evidence

Compliance documentation and evidence
The paperwork is where many contractors stall. We produce and maintain it so your assessment is a review, not a rebuild.
Build and update your System Security Plan
Maintain a Plan of Action and Milestones and your SPRS score inputs
Keep a complete, audit-ready evidence package
How the CMMC engagement works
Getting to a passing score follows a clear, predictable path. Here is how a GenCare CMMC engagement runs from first call to maintained compliance.
1
Step 1: 30-minute readiness assessment
At no cost, we discuss your users, devices, applications, networks, locations, and the contracts driving your CMMC requirement, and begin a gap analysis against the 110 NIST SP 800-171 controls. You leave with a clear picture of your level and your scope.
2
Step 2: Scope and quote
We map where your Controlled Unclassified Information lives and set your assessment boundary, then quote one flat monthly price per employee that includes the software, setup, and maintenance you need.
3
Step 3: Onboarding and control build
Over roughly two months, we enroll and control your devices, secure your email and identities, block un-enrolled devices, and train your users, while standing up logging, backup, and monitoring.
4
Step 4: Self-assessment success and ongoing management
Our meetings guide you to a passing Level 2 self-assessment, typically within six months, and we maintain the controls, evidence, and documentation from there, supporting any third-party assessment your contracts require.
Who we serve
GenCare works with operations-heavy organizations across Greater Los Angeles, typically between 50 and 250 employees. Our CMMC work fits the aerospace and defense suppliers clustered around El Segundo and the South Bay, manufacturers in the defense supply chain, professional services firms handling government data, and the subcontractors who support primes. We bring the same local, hands-on support to compliance that we bring to Microsoft 365 services and day-to-day IT help desk support for clients from Glendale and Pasadena to Downtown LA and Irvine.
Straightforward, Flat-Rate CMMC Pricing for LA Contractors
Most CMMC providers hide their pricing until you are deep in a sales process. We do not. After your readiness assessment, GenCare quotes one flat monthly price per employee. That price includes the software, the setup, and the ongoing maintenance for the technical controls we own, so your budget is predictable from the start.
You work with a local Los Angeles IT services company, Microsoft Solutions Partner expertise, and an owner on every ticket, because every GenCare employee owns a piece of the company. We have protected Los Angeles businesses since 1986, and some of our clients have been with us for more than 25 years.
No cost and no obligation to assess your current state
One flat monthly price per employee, quoted up front
A local Southern California team with a 15-minute response target
Protecting Los Angeles defense contractors, on-site and remotely
GenCare provides CMMC compliance services in Los Angeles and hands-on cybersecurity support to organizations across Greater Los Angeles, including Glendale, Pasadena, Burbank, Santa Monica, Downtown LA, and Irvine. We are employee-owned, Los Angeles-based since 1986, and ready to build the compliance foundation your contracts depend on.
Frequently asked CMMC questions
What is CMMC compliance?
CMMC compliance means meeting the Cybersecurity Maturity Model Certification standard the Department of Defense requires of its contractors. It verifies that your company protects Federal Contract Information and Controlled Unclassified Information to a defined level before you are awarded a contract. For most contractors, that is Level 2, built on the 110 controls in NIST SP 800-171.
What is CMMC Level 2, and who needs it?
CMMC Level 2 is the advanced tier that applies to any contractor or subcontractor handling Controlled Unclassified Information. It requires all 110 security controls from NIST SP 800-171, covering access control, encryption, monitoring, training, and more. If your defense contracts mention CUI or DFARS clause 252.204-7012, you almost certainly need Level 2.
Do I need third-party certification, or can I self-assess?
It depends on your contract. Some Level 2 acquisitions allow an annual self-assessment, where you attest to meeting all 110 controls. Others require certification by an accredited third-party assessment organization, a C3PAO, every three years. GenCare prepares you fully for either, and supports you through the assessment when one is required.
What is NIST SP 800-171, and how does it relate to CMMC?
NIST SP 800-171 is the federal publication that defines 110 security requirements for protecting Controlled Unclassified Information on non-government systems. CMMC Level 2 is essentially the verification mechanism for those requirements. Your compliance is measured as a score against the 110 controls and filed in the Supplier Performance Risk System, known as SPRS.
How much does CMMC Level 2 compliance cost?
Cost depends on your size, your scope, and how far your current systems already meet the standard. GenCare removes the guesswork by scoping first, then quoting one flat monthly price per employee that includes software, setup, and maintenance for the technical controls we manage. Tight scoping, limiting the work to systems that actually touch CUI, is the single biggest lever on cost.
How long does it take to become CMMC compliant?
For a typical Los Angeles contractor, GenCare guides you to a passing Level 2 self-assessment within about six months. The first two months cover onboarding and standing up the technical controls, and the remaining time is spent completing your administrative controls, gathering evidence, and validating that everything holds.
What does GenCare handle, and what stays with our team?
GenCare owns the technical controls, the majority of the 110, plus the process, the documentation, and the evidence. Your team keeps the roughly two dozen administrative and physical controls only you can perform: assigning internal roles, screening and training staff, and securing your facilities. We guide those in our meetings, so your weekly involvement stays near five hours during the build.
